Is Your Business VPN Obsolete? The Shift to Zero Trust Explained
The question “is VPN obsolete?” shows up in every security meeting now — and the honest answer is neither “yes” nor “no.” VPNs are being replaced at the top of the stack for sensitive, cloud-native, contractor-heavy, BYOD environments. They are being hardened and retained for legacy apps, IoT coverage, small teams, and traffic encryption. The market has split: new remote-access deployments tilt heavily toward Zero Trust Network Access (ZTNA), while existing VPN stacks are being layered with identity, segmentation and policy controls rather than thrown away.
This article walks through exactly what changed, why the headlines exaggerate, where a VPN is still the right tool, and the hybrid playbook most teams in 2026 are actually running. If you want the deeper head-to-head comparison, jump to our Business VPN vs Zero Trust guide.
Is VPN Obsolete in 2026?
Not as a concept, yes as a default. A plain, trust-after-authentication VPN is becoming obsolete for sensitive remote-access workloads. Gartner predicted at least 70% of new remote-access deployments would be served predominantly by ZTNA — and 2026 market data is tracking that forecast closely. But a well-hardened VPN paired with identity, segmentation and continuous verification is not obsolete at all; it is the baseline layer most hybrid deployments still run on.
Short version: VPNs are not dead. The old assumption that a tunneled user is “trusted” is. Keep the VPN for what it does best — traffic encryption, IoT coverage, legacy network access — and put ZTNA or identity-layer controls in front of the apps where a compromised laptop would actually hurt you.
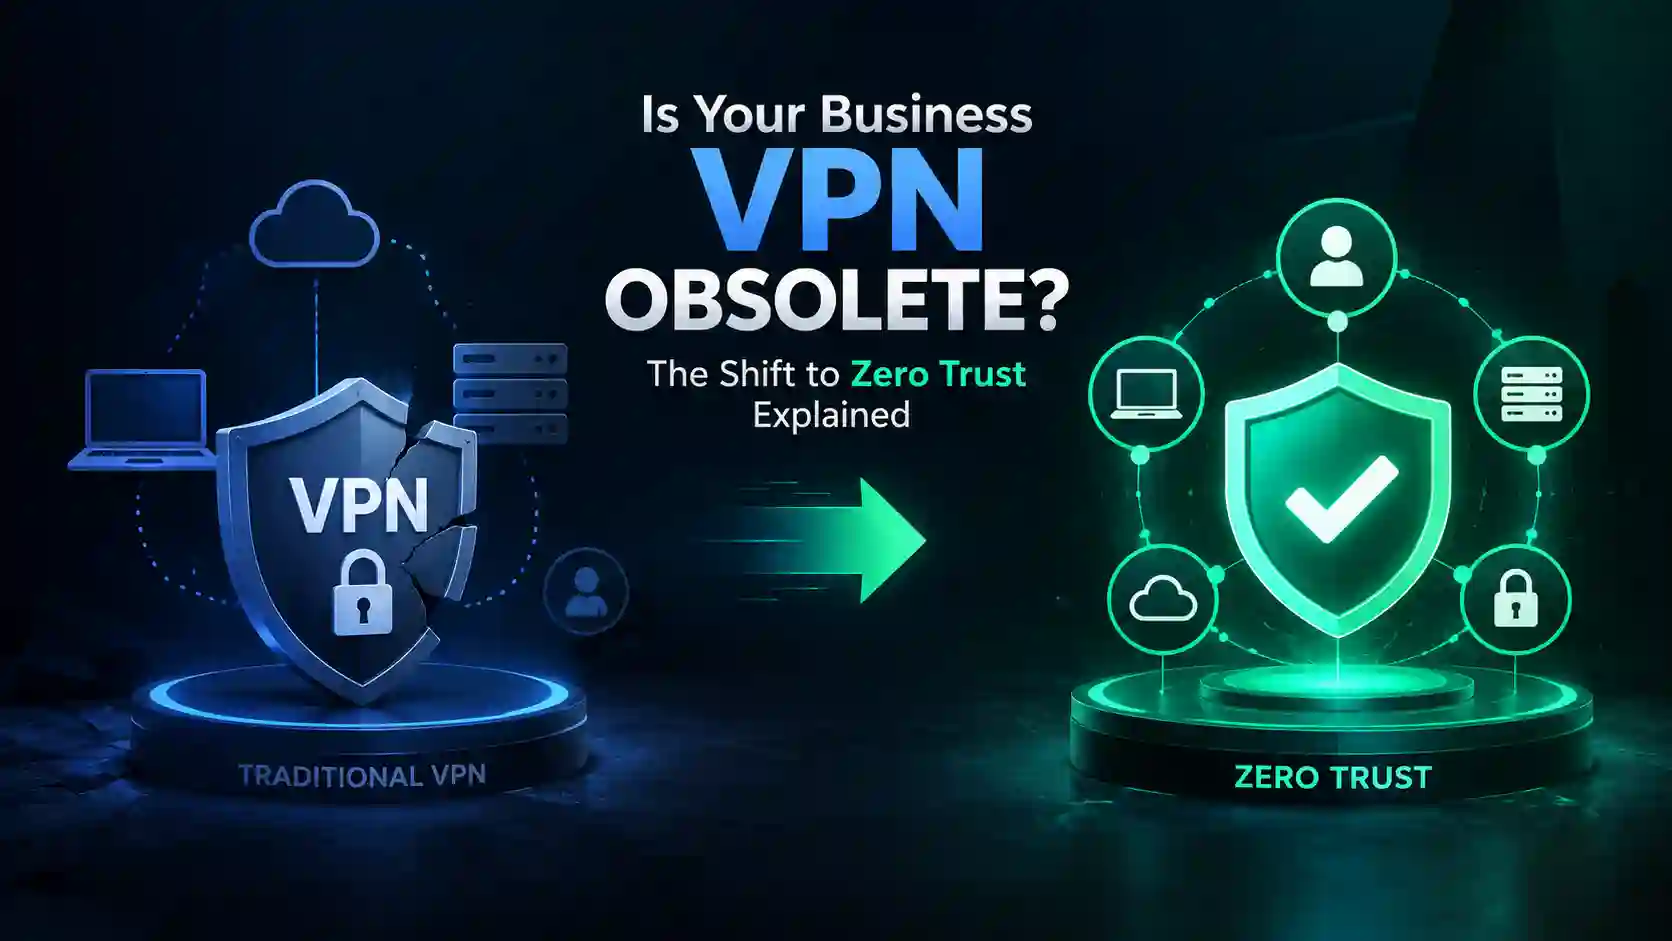
Table of Contents
- Why the question is being asked now
- The forecast: what Gartner actually said
- The security gap VPNs cannot close
- What Zero Trust actually changes
- Where VPNs are still the right tool
- Adoption vs reality: the maturity gap
- The hybrid play most teams land on
- 6-step migration playbook
- Cost comparison at three scales
- How we scored the shift
- FAQs
- Final verdict
- Sources & research notes
ContextWhy the “Is VPN Obsolete?” Question Is Being Asked Now
Three forces converged between 2020 and 2026 and made the old VPN assumption uncomfortable for anyone running a real business:
- Remote work became the default, not the exception. Millions of employees now work from home Wi-Fi, cafés, co-working spaces and hotels — networks the business does not control.
- Apps moved off the corporate network. SaaS, cloud workloads, APIs and contractors mean most sensitive work no longer lives behind a single corporate firewall. A tunnel into the “corporate network” reaches fewer of the resources people actually use.
- Attackers started targeting VPN infrastructure directly. A 2025 ScienceDirect study documented a 238% surge in VPN-targeted attacks between 2020 and 2022, and high-profile edge-VPN exploits kept that pressure on through 2024 and 2025.
Put those three together and the old trust model — authenticate once, grant broad network access, trust the tunnel — starts to look like a risk you are paying for rather than one you are closing. That is why the question keeps getting asked, and why it is being answered differently depending on the size and shape of the team.
The forecastWhat Gartner Actually Said (and What It Did Not Say)
The headline you see everywhere — “Gartner: 70% of new remote-access deployments will be served by ZTNA” — is real, but the full statement matters more than the number. Gartner’s forecast is about new deployments, not rip-and-replace of existing, well-hardened stacks. It is also about deployments being predominantly served by ZTNA, which usually means ZTNA fronting the sensitive apps, not ZTNA being the only technology on the network.
Two other predictions from the same research thread are worth knowing:
- By 2026, about 65–70% of organizations are expected to adopt Zero Trust as a core cybersecurity strategy.
- Only roughly 10% of large enterprises are predicted to have a mature, measurable Zero Trust program by 2026 — most are still in progress.
Translation: the market direction is unambiguous, but most teams are somewhere in the middle, not at the end state. That gap between intent and maturity is exactly where the hybrid playbook earns its keep.
Share of new remote-access deployments: ZTNA vs traditional VPN
Directional market shift, based on Gartner forecast and 2025–2026 industry surveys. Green = traditional VPN share, purple = ZTNA-predominant share.
Illustrative trajectory aligned to Gartner’s 70% forecast for new deployments by 2025+. Existing, hardened VPN stacks are not included in the “replaced” share.
The gapThe Security Gap a Plain VPN Cannot Close
A business VPN encrypts traffic between a user and a gateway. That is valuable — and it still matters. What it does not do, by design, is decide what that user may touch once the tunnel is up. That decision is pushed to everything behind the gateway: firewalls, network segmentation, application authorization, IAM.
When that downstream stack is strong, a VPN is a perfectly fine access layer. When it is not — which, in most real businesses, is most of the time — the VPN becomes the path attackers use to move laterally. Three concrete failure modes keep showing up in incident reports:
- One compromised laptop = broad network reach. A phishing hit or a stolen session on a tunneled user often grants access to shared drives, internal services, databases and printers that have nothing to do with the victim’s role.
- Contractors and BYOD inherit too much. Handing a contractor network-level VPN access is almost always more permission than their work requires.
- Edge-VPN devices are a favorite attacker target. The 238% surge in VPN-targeted attacks reflects how often VPN gateways themselves — and their management interfaces — end up on the shortlist.
None of this means VPNs are useless. It means a VPN is not a security model; it is a transport. The security model has to come from somewhere else, and in 2026 that “somewhere else” is increasingly a Zero Trust control plane.
The replacementWhat Zero Trust Actually Changes
Zero Trust Network Access flips the assumption: no user, device or request is trusted by default, even if it came from inside a tunnel. Every access is evaluated — identity, device posture, location, application, policy — before the request is brokered to a specific resource. The user does not land on a broad network; they are connected straight to the app they are allowed to use.
Tunnel first, trust later
Authenticate → open tunnel → land on network → rely on downstream firewalls and ACLs to limit reach.
- One authentication at tunnel start
- Broad network access by default
- Security depends on what sits behind the gateway
- Good at encrypting traffic, weak at authorizing requests
Verify first, broker later
Every request is checked against identity, device posture and policy before being brokered to a specific app or service.
- Continuous verification on every request
- Least-privilege access by design
- Internal services hidden unless explicitly allowed
- Good at authorizing requests, still needs encryption underneath
The practical effect: a compromised laptop that was authorized for the ticketing system at 9am can lose that access at 9:15am the moment device posture fails — without anyone touching a firewall rule. That is the property most incident responders want and that a plain VPN cannot give you.
The realityWhere a VPN Is Still the Right Tool
The “is VPN obsolete” framing oversimplifies because there are several jobs a VPN still does better than ZTNA, or does in addition to ZTNA. If your team fits any of these, a VPN is not obsolete — it is a required layer.
| Use case | Why a VPN still fits | Example teams |
|---|---|---|
| Traffic encryption on untrusted networks | VPNs are purpose-built to encrypt all traffic in transit. ZTNA brokers app access; it does not generally encrypt the whole connection. | Remote workers on café and hotel Wi-Fi — see our best VPN for remote workers guide. |
| IoT and device coverage | Printers, cameras, smart TVs and consoles cannot run a ZTNA agent. A VPN on the router covers them in one tunnel. | Small offices, home offices — see best VPN routers. |
| Legacy on-prem apps | Many internal tools expect a network, not a brokered app session. Rewriting or wrapping them for ZTNA is not always realistic. | Manufacturing, finance, healthcare with old ERPs. |
| Small-team economics | A well-hardened business VPN at a few dollars per seat plus enforced MFA covers most remote-access risk for teams under ~50. | Founder-led teams — see best VPN for remote teams. |
| Journalists, activists, humanitarian workers | Hiding location and traffic on hostile networks is still a VPN-shaped job; ZTNA gates apps, not connections. | See best VPN for journalists, best VPN for activists, best VPN for humanitarian workers. |
| Development and self-hosted tools | Engineers often need fast tunnel access to build servers, databases and dev environments. ZTNA can sit on top for production. | See best VPN for developers. |
The honest read: “VPN obsolete” is a marketing frame. “Plain trust-after-authentication VPN as the only remote-access layer for a modern enterprise” is the thing that is actually becoming obsolete.
AdoptionIntent vs Maturity: The Gap Most Teams Are In
Adoption surveys tell one story; implementation surveys tell another. Across 2025 and 2026 research, the pattern is consistent:
- ~82% of organizations express intent to adopt Zero Trust in some form.
- ~65–70% plan to make Zero Trust a core cybersecurity strategy by 2026.
- Only ~10–17% report having a mature, measurable, full-scope Zero Trust program.
The gap is not hypocrisy; it is reality. ZTNA needs an identity platform, policy discipline, device-posture plumbing, connectors, logging and a change in how offboarding and access requests work. Most teams are partway through, not done. That is the strongest argument for a hybrid approach: start moving toward Zero Trust without pretending the journey is a cutover.
Zero Trust: intent vs real maturity (share of organizations)
Illustrative, based on 2025–2026 industry surveys including Gartner and the ORDR Zero Trust Statistics 2026 report.
The gap between the two lines is where most teams actually live in 2026 — planning and piloting, not operating.
The playThe Hybrid Play Most Teams Land On
The pattern we see most often in 2026 is not “replace the VPN” but “add a control plane in front of the apps that matter.” The stack ends up looking like this:
- Business VPN for general remote access. Encrypts traffic, covers IoT, gives stable egress. Teams pick a strong provider — Surfshark at the value end, NordVPN or ExpressVPN for performance, Proton VPN for privacy-first teams.
- ZTNA in front of the sensitive apps. Finance, HR, customer data, source code, admin consoles and production environments are brokered by identity and device posture, not by a tunnel.
- One identity platform as the source of truth. Same IdP issues the session for the VPN and the ZTNA broker, so offboarding is one action.
- Device posture gates on both layers. A non-compliant device can be routed to a limited VPN profile and refused ZTNA access entirely.
This hybrid is the shape the Gartner forecast actually describes: ZTNA serving the majority of new remote-access use cases, VPN retained for legacy paths and traffic encryption. It also lets you run the migration incrementally instead of betting the company on a cutover.
Low-risk starting point: keep your current VPN, put ZTNA in front of your three most sensitive apps, and measure what you actually learn before committing the whole network.
Start with Surfshark for Your Team →Playbook6-Step Migration Playbook: From Plain VPN to Zero Trust (or Hybrid)
Two supporting guides that plug into specific steps: for small-business teams who only need a hardened VPN baseline, see our best cheap VPN list; for teams evaluating the full architecture trade-off, read the deeper Business VPN vs Zero Trust comparison.
CostWhat Each Path Actually Costs at 10, 100 and 1,000 Seats
Sticker prices mislead because VPNs and ZTNA platforms are priced differently. Business VPNs are typically per-seat licenses; ZTNA vendors charge per user plus infrastructure (connectors, identity integration, logging). At small scale, a business VPN is dramatically cheaper. At enterprise scale the gap narrows — and the cost of a single breach usually dwarfs the annual ZTNA bill.
Estimated annual spend by team size (USD)
Illustrative ranges for a hardened business VPN vs a ZTNA deployment at three team sizes. Green = VPN, purple = ZTNA. Editorial estimates, September 2026.
At 10 seats, a hardened business VPN can be 7–8× cheaper. At 1,000 seats the ZTNA stack is typically several times more expensive — but its breach-prevention value compounds.
Where your budget should go, by team profile
Editorial scoring: how much of your remote-access budget should lean on VPN vs ZTNA.
- 25% — Small SaaS teams: VPN-heavy, ZTNA only for 2–3 sensitive apps
- 30% — Mid-size growing companies: balanced hybrid, ZTNA on customer data + code
- 23% — Regulated enterprises: ZTNA-first, VPN retained for legacy paths
- 14% — Distributed global teams: ZTNA for contractors + BYOD, VPN for traffic encryption
- 8% — Identity, logging and posture tooling shared by both layers
MethodologyHow We Scored the Shift
We evaluated the “is VPN obsolete?” question across the dimensions that actually drive enterprise buying decisions: security model, access granularity, deployment complexity, cost at three seat sizes, user experience, legacy-app fit, BYOD/contractor fit and maturity. Editorial weights:
- 30% — Security model & least-privilege posture
- 20% — Access granularity (per-app vs per-network)
- 20% — Deployment complexity & cost at scale
- 15% — User experience & friction
- 15% — Maturity, ecosystem and vendor stability
FAQsIs VPN Obsolete? Frequently Asked Questions
Is VPN obsolete in 2026?
Should I replace my business VPN with ZTNA?
What is the biggest security gap in a plain business VPN?
Why are VPNs still being attacked if they are being replaced?
What is the cheapest way to move toward Zero Trust?
Do small businesses need Zero Trust?
What does ZTNA not replace a VPN for?
Which VPN should I start with while I plan the ZTNA move?
Is Your Business VPN Obsolete? The Honest 2026 Answer
The is VPN obsolete question has a real answer, and it is not a soundbite. A plain, trust-after-authentication VPN is becoming obsolete as the only remote-access layer for modern businesses — Gartner’s forecast that 70% of new deployments will be ZTNA-predominant is tracking closely in the field. But a well-hardened VPN is not obsolete; it is the baseline layer most hybrid deployments still run on. The right move for most teams in 2026 is layered: keep a strong business VPN (Surfshark for budget teams, NordVPN or ExpressVPN for performance, Proton for privacy-first shops), harden it properly, and put Zero Trust in front of the three to ten apps where a compromised laptop would actually hurt. Expand ZTNA app-by-app in sensitivity order; retire VPN paths only when every dependent device and application has a proven alternative.
| Team size | Primary access layer | Where ZTNA earns its keep | First move |
|---|---|---|---|
| 2–15 people | Hardened business VPN | Almost never yet — focus on MFA, endpoint and app permissions | Start with Surfshark |
| 15–100 people | VPN + ZTNA on sensitive apps | Customer data, finance, HR, source code, admin consoles | Pilot ZTNA on 3 apps |
| 100–1,000+ | ZTNA-first, VPN for legacy paths | Contractors, BYOD, regulated data, global teams | Identity platform first |
Disclosure: This article contains affiliate links. If you purchase through them, we may earn a commission at no extra cost to you. Market statistics are drawn from Gartner forecasts, IBM / Ponemon breach reports, ScienceDirect research on VPN-targeted attacks, and 2025–2026 industry adoption surveys cited in the sources. Pricing and product behavior change quickly — confirm current terms on vendor sites before committing, especially annual contracts.
Sources & Research Notes
Architecture comparisons draw on vendor documentation and peer-reviewed security research; market forecasts come from Gartner and industry surveys. Editorial scores and cost estimates are our own judgments, verified September 2026.
- Gartner Market Guide for Zero Trust Network Access: forecast that at least 70% of new remote-access deployments will be served predominantly by ZTNA rather than VPN services — cited inline in the quick answer and forecast section.
- Gartner / industry surveys (2025–2026): approximately 65–70% of organizations expected to adopt Zero Trust as a core cybersecurity strategy by 2026; only ~10% of large enterprises predicted to have a mature, measurable Zero Trust program by 2026.
- ORDR Zero Trust Statistics 2026 report: ~82% adoption intent vs ~17% full implementation — cited in the intent-vs-maturity section.
- IBM / Ponemon Institute, Cost of a Data Breach Report: global average breach cost around $4.88 million in 2024, rising in the 2025 and 2026 editions — cited in the stat strip.
- ScienceDirect (2025), “A study on the VPN security landscape post Covid-19” (K. Qollakaj, cited by 10): documented a 238% surge in VPN-targeted attacks between 2020 and 2022 — cited inline in the security-gap section.
- Vendor and industry reference for architectural comparison: Fortinet, Cato Networks, Duo/Cisco, NordLayer, Verizon Business, OpenVPN and Cloudbrink comparison pieces on ZTNA vs VPN published 2024–2026.
- MarketsandMarkets, Mordor Intelligence, SNS Insider, Grand View Research: ZTNA market sizing and CAGR forecasts (2025–2033) — used to contextualize the market shift.
Editorial cost ranges and scoring weights are our own estimates. Actual ZTNA and VPN pricing depends on seat count, deployment model, identity platform and support tier — always confirm current terms with vendors before committing.